Login lockout
Five failed logins in five minutes locks the address out for an hour.
Witen Blocker for WordPress
A free security plugin that starts protecting your site the moment you activate it, with two-factor sign-in, crawler-by-crawler control over AI bots, and file scans when you want more. Works on any host, including shared hosting.
Version 0.6.55 · WordPress 6.2+ · PHP 8.1+ · Free from the WordPress Plugin Directory. No account needed.
Coming from another plugin? Compare it with Wordfence or WP fail2ban.
WordPress 0.6.50. Captured from an isolated test installation with demonstration accounts.
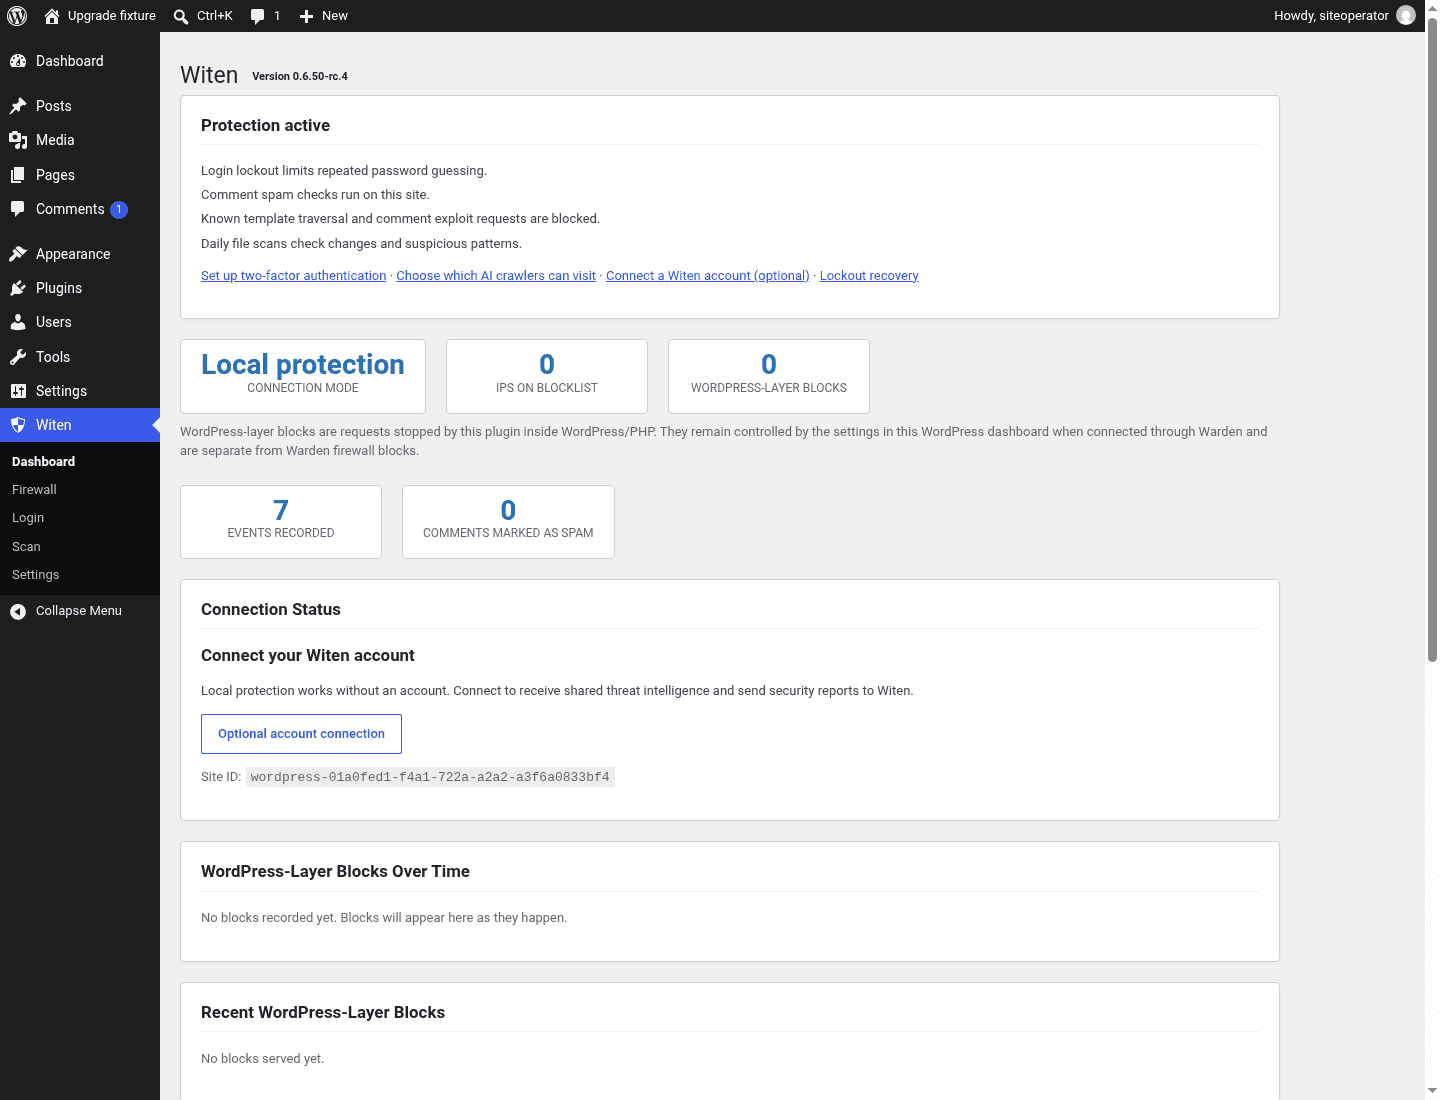
No setup wizard, no account. These run straight away with defaults that suit most sites.
Five failed logins in five minutes locks the address out for an hour.
Requests for published WordPress exploits are refused before they reach the vulnerable code.
A hidden field and a timing check catch bots. No comment text leaves your site.
A daily scan flags new and changed files and known malware patterns for you to review.
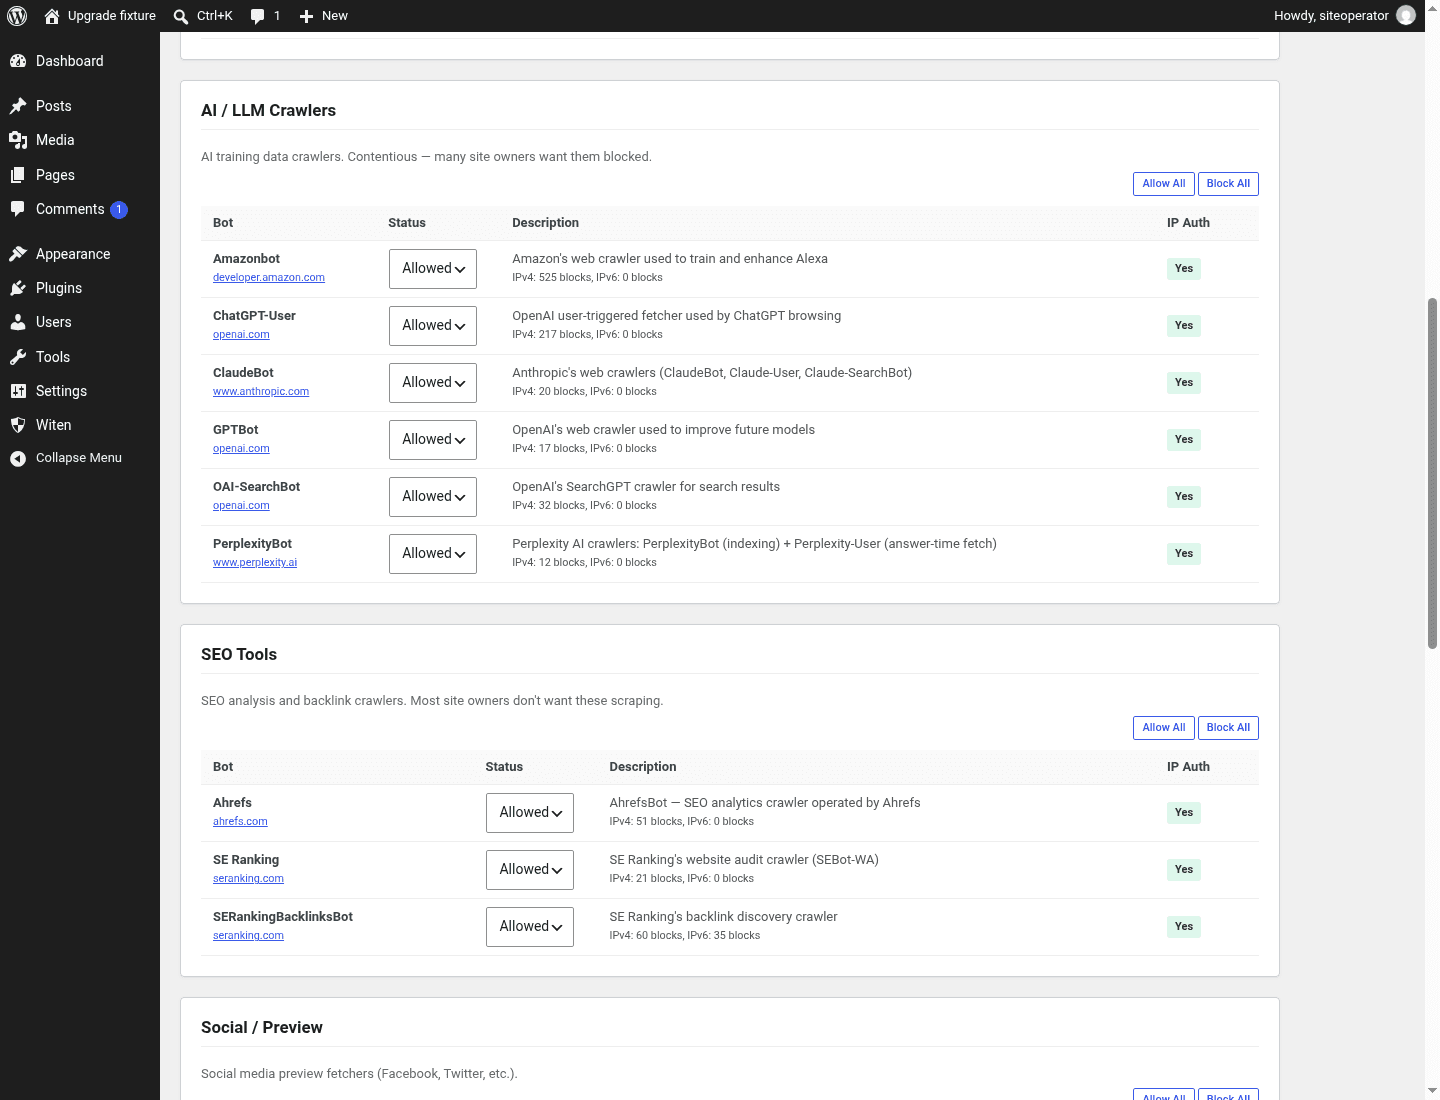
Welcome every AI crawler, block them all, or pick one by one. Every recognised crawler gets its own allow or block switch, and nothing is blocked until you choose.
Crawlers are recognised by their published network ranges as well as their user agent, so a scraper pretending to be Googlebot doesn't get Googlebot's pass.
Plus the major search engines and ten uptime monitors, so a rule for one bot never catches the services you rely on.
Each user can add an authenticator app and print recovery codes. A stolen password alone no longer opens your dashboard.
Move the login page to a URL only you know, harden .htaccess, keep your own block and allow lists, and turn away clients with no user agent. With a connected account you can also block Tor exit nodes.
Connect a free Witen account with a one-time setup token and your site receives blocklists built from attacks seen across every Witen site and server.
Run WordPress on your own Linux server? Add Warden and the plugin's findings become firewall blocks, stopping repeat attackers before they reach PHP.